Predicting and Preventing Hospital Data Breaches
Due to the high value of healthcare data, breaches in this sector are currently the fastest-growing form of cybercrime. What factors influence the occurrence of these breaches?
Importance of healthcare data and occurrence of breaches
Healthcare data holds significant value to criminal organizations, surpassing even the black market value of credit card data. It includes a variety of personal information such as names, social security numbers, dates of birth, protected health information, and, depending on the health system, credit card information [1]. The value of healthcare data contributes to a high number of cyberattacks. In 2023, the healthcare industry reported 809 data breaches, the highest among all industries in the USA [2]. Data breaches can be categorized as theft, loss, improper disposal, unauthorized access or disclosure, and hacking [3].
An analysis of data breaches of hospitals in the US from 2011 to 2015 indicates that data breaches might even reduce the quality of patient care [4]. To mitigate data breaches and safeguard protected health information, laws like HIPAA (Health Insurance Portability and Accountability Act) were enacted [5]. One component of HIPAA is risk assessment, which entails evaluating the likelihood and impact of specific cyber threats [6]. However, as of 2019, a majority of covered entities had not met the statutory risk management requirements, resulting in financial penalties [7]. Consequently, research aiding healthcare providers in performing adequate risk management is of high importance.
Likelihood and factors contributing to data breaches in healthcare
Dolezel et al. conducted an investigation on how internal and external factors influenced the occurrence of data breaches in the United States. Using predictive modeling,Machine learning is an iterative process and is classified as a subcategory within the field of Artificial Intelligence. Algorithms are programmed to initially learn from datasets and can subsequently develop in a self-learning manner without further explicit intervention. Accordingly, predictions are generated by algorithms based on retrospectivel… Explained in the video. they analyzed data of 3,233 US-counties, of which 1,032 had reported data breaches (8).
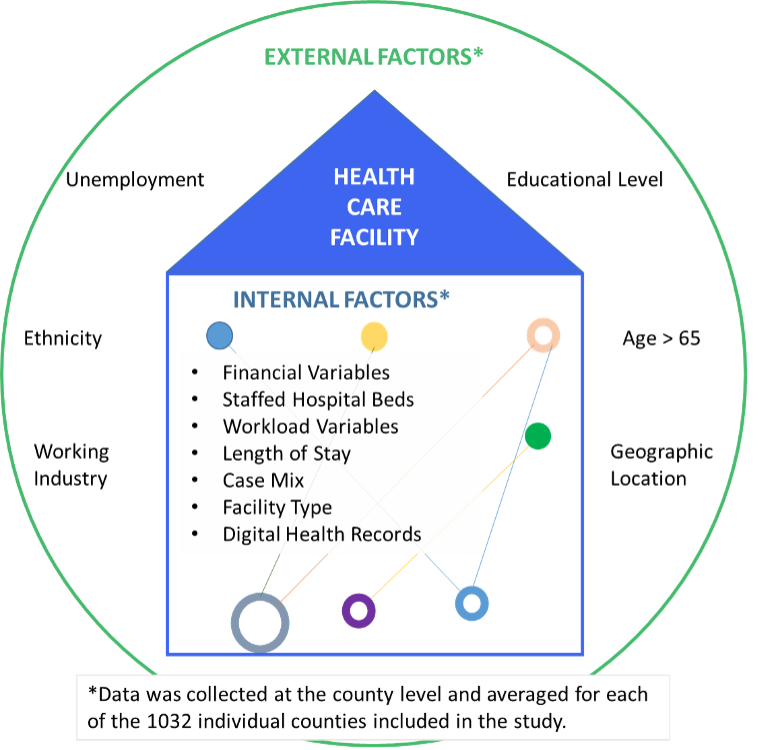
Figure 1: Internal and external factors that influence the occurrence of data breaches on healthcare facilities
The findings showed that inpatient workload, facility type, and financial factors had the greatest impact on data breaches:
Inpatient workload describes a combination of the number of acute care beds, bed percentage use, and the severity of cases. A high inpatient workload may lead to higher efforts for patient care, making human errors more likely and also increasing the amount of processed data [8]. Medical centers and pediatric trauma centers were facility types especially prone to cyberattacks. They are mostly located in urban areas, where more patients can be served and more data is processed, making them more attractive to cybercriminals. Additionally, US medical centers often offer free medical treatment to populations without adequate access to healthcare and therefore might have fewer resources for cybersecurityCybersecurity represents an extension of information security. It goes beyond the boundaries of traditional information security and encompasses, in addition to the protection of information resources, also the protection of other assets including the individual. In cybersecurity, the human factor gains an additional dimension: the person as a pote… Explained in the video. protection. [8]. High accounts receivable and operating income were financial factors that led to an increased number of cyberattacks in the respective counties. Dolezel et al. concluded that higher profitability increases the attractiveness of hospitals to cybercriminals. Conversely, hospitals with high profit margins and the ability to allocate higher expenditures had lower risks of data breaches, likely due to their capability to procure adequate staff and infrastructure [8].
Conclusion
The healthcare industry is a primary target for cybercriminals, necessitating robust protective measures. Comprehensive security programs should encompass governance, awareness, education, internal controls, training, as well as monitoring and evaluation [9].
Current research highlights the human factor in data security, advocating for additional security measures such as hiring bilingual technical support staff in regions with language barriers and providing additional training or handouts for patients, visitors, and elderly individuals on their cybersecurityCybersecurity represents an extension of information security. It goes beyond the boundaries of traditional information security and encompasses, in addition to the protection of information resources, also the protection of other assets including the individual. In cybersecurity, the human factor gains an additional dimension: the person as a pote… Explained in the video. roles [8].

Contact
E-Mail:
atlas-itg@uni-wh.deInnovation in Healthcare
Alfred-Herrhausen-Straße 50
58448 Witten, Germany